When a familiar voice is not enough
Reuters reported on September 25, 2026 that an impersonation scam had targeted Fideuram’s then-chairman, Paolo Molesini, beginning in February. According to sources cited by Reuters, a WhatsApp message impersonated Intesa Sanpaolo CEO Carlo Messina and a subsequent call used an AI-replicated voice to impersonate a senior lawyer. Sources put the transfers at approximately EUR 95 million, with roughly EUR 53 million recovered and EUR 36 million still missing at the time of reporting. The banks declined to comment. These are attributed reporting details, not a bank-confirmed technical investigation or an updated account of recovery. Reuters report, September 25, 2026 (via MarketScreener).
The sequence matters: executive impersonation, urgency, a familiar intermediary, and a request routed through a legitimate business function. These are established social-engineering techniques. AI voice cloning can make the story more convincing, but the organization’s authorization design determines whether a persuasive impersonation can become a payment. For CTOs and CIOs, the key question is not whether every employee can identify a synthetic voice. It is whether an unverified communication can trigger an irreversible, high-impact action.
Design controls around the transaction
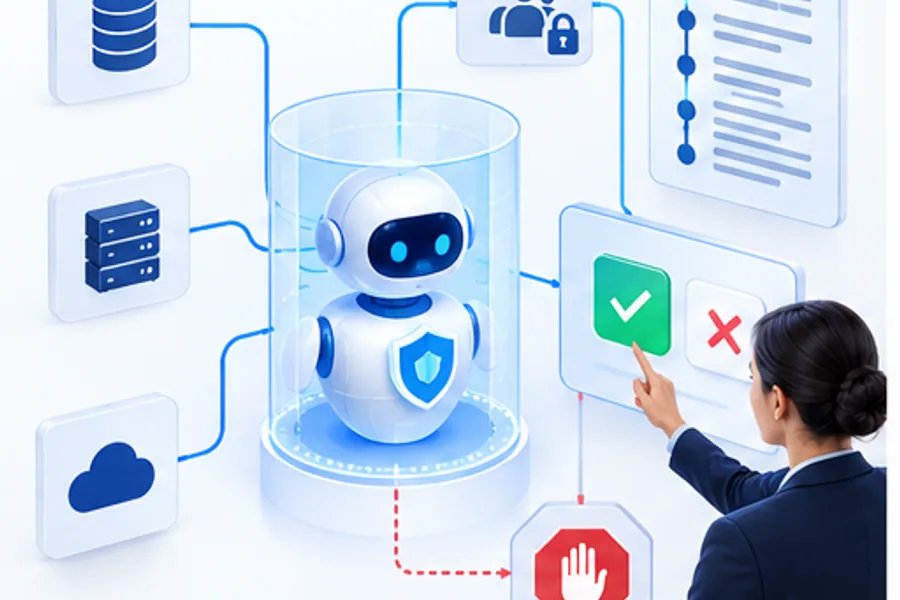
A call, video meeting, email, or chat may initiate a payment request; it should not approve the payment by itself. High-value transfers should be created and authorized in a governed treasury or ERP workflow, with an auditable record of the requester, reviewers, beneficiary, amount, and release decision. This separates the identity signal from the authority to move funds. A person who sounds like an executive may still be an impostor, while the payment system continues to enforce the same control requirements.
Explore: Security and control capabilities
Six controls that make impersonation harder to monetize
1. Verify through a pre-established independent channel. For high-risk requests, use contact details maintained in a trusted corporate directory or approved procedure. Do not call a number supplied in the suspicious message, and do not continue verification in the same chat. A second channel is useful only when it is independently established.
2. Require separation of duties. Use maker-checker controls so the person preparing a transfer cannot release it alone. Set approval thresholds according to amount, beneficiary risk, jurisdiction, and deviations from normal behavior. Apply the policy to every role, including the CEO, chairperson, and CIO. Any emergency exception should require a separate approver, a documented reason, and a post-event review.
3. Bind approval to the payment details. Show the beneficiary, account, amount, currency, purpose, and recent changes in the approval interface. Avoid generic prompts such as “Approve transaction?” Where the platform supports it, use a cryptographically protected approval tied to the specific transaction. Account login or a one-time code may confirm access, but does not necessarily demonstrate that the approver reviewed the exact recipient and amount.
4. Put friction around beneficiary changes. A new payee, changed account, unusual destination, or altered payment procedure should trigger additional review and, where business needs allow, a cooling-off period. Maintain trusted beneficiary records and alert treasury when a change and a high-value transfer occur close together.
5. Detect anomalies and pause before release. Treasury systems can flag unusual amounts, geographies, timing, channels, or approval patterns. Risk signals should route a payment to a human review or hold state, not make an unsupported accusation. Deepfake classifiers can contribute evidence, but should not be the sole control: they can miss convincing fakes, flag legitimate media, and become less reliable as methods change.
6. Harden identity and communications. Protect executive email, collaboration platforms, and payment administration with phishing-resistant authentication where supported, least privilege, monitored account changes, and strong recovery procedures. Limit unnecessary access to payment workflows and monitor suspicious sign-ins, forwarding rules, and newly registered devices.
A practical control matrix for technology leaders
A control is useful only when it has an owner, an observable outcome, and a response path. CTOs should work with treasury, finance, security, and business leadership to map each risk to a system control and evidence that it is operating. The matrix below is a starting point; thresholds and approval requirements should be set through the organization’s risk and regulatory process.
Implement in stages, then exercise the response
Begin with a short discovery across treasury, finance, security, identity, and executive support. Map how payment instructions arrive, who can create and approve them, which systems can release funds, and where beneficiary details are maintained. Identify high-value and hard-to-reverse paths first. Then close obvious gaps: remove single-person release paths, establish trusted callback details, add review for new beneficiaries, and make approval records searchable.
Next, connect risk signals to operational actions. Define which events require an alert, a hold, a second approval, or a bank callback. Ensure that logging captures enough to investigate without retaining unnecessary sensitive content. Set owners and service expectations for alerts so a high-risk payment does not wait in an unattended queue. Test the controls in a safe environment and confirm that legitimate urgent payments still have a governed route.
Finally, rehearse the first hour of a suspected incident with treasury, security, IT, legal, communications, and executive leadership. Staff should know who can pause pending payments, contact the sending and receiving banks, preserve messages and call records, and activate incident response. Tabletop exercises should combine channels: a message followed by a call, a familiar voice, a new beneficiary, and pressure to keep the request confidential.
Explore: AI security and operations services
Make trust verifiable
The Fideuram case is a reminder that AI can make impersonation more persuasive, but the deeper issue is relying on identity signals that were never designed to authorize high-value transactions. A resilient organization verifies identity independently, separates request from approval, binds authorization to payment details, monitors for anomalies, and rehearses recovery.
FIX Intelligence, part of FIX Solutions JSC, helps organizations assess AI-related risks and design secure workflows, governance, and operational controls around production systems. A focused review can map where AI-enabled impersonation intersects with payment, identity, and approval processes, then prioritize controls according to business impact. The goal is not to promise that every fake can be detected; it is to ensure that a convincing voice is still not enough to move money.