Agentic AI in 2027: orchestration becomes the product question
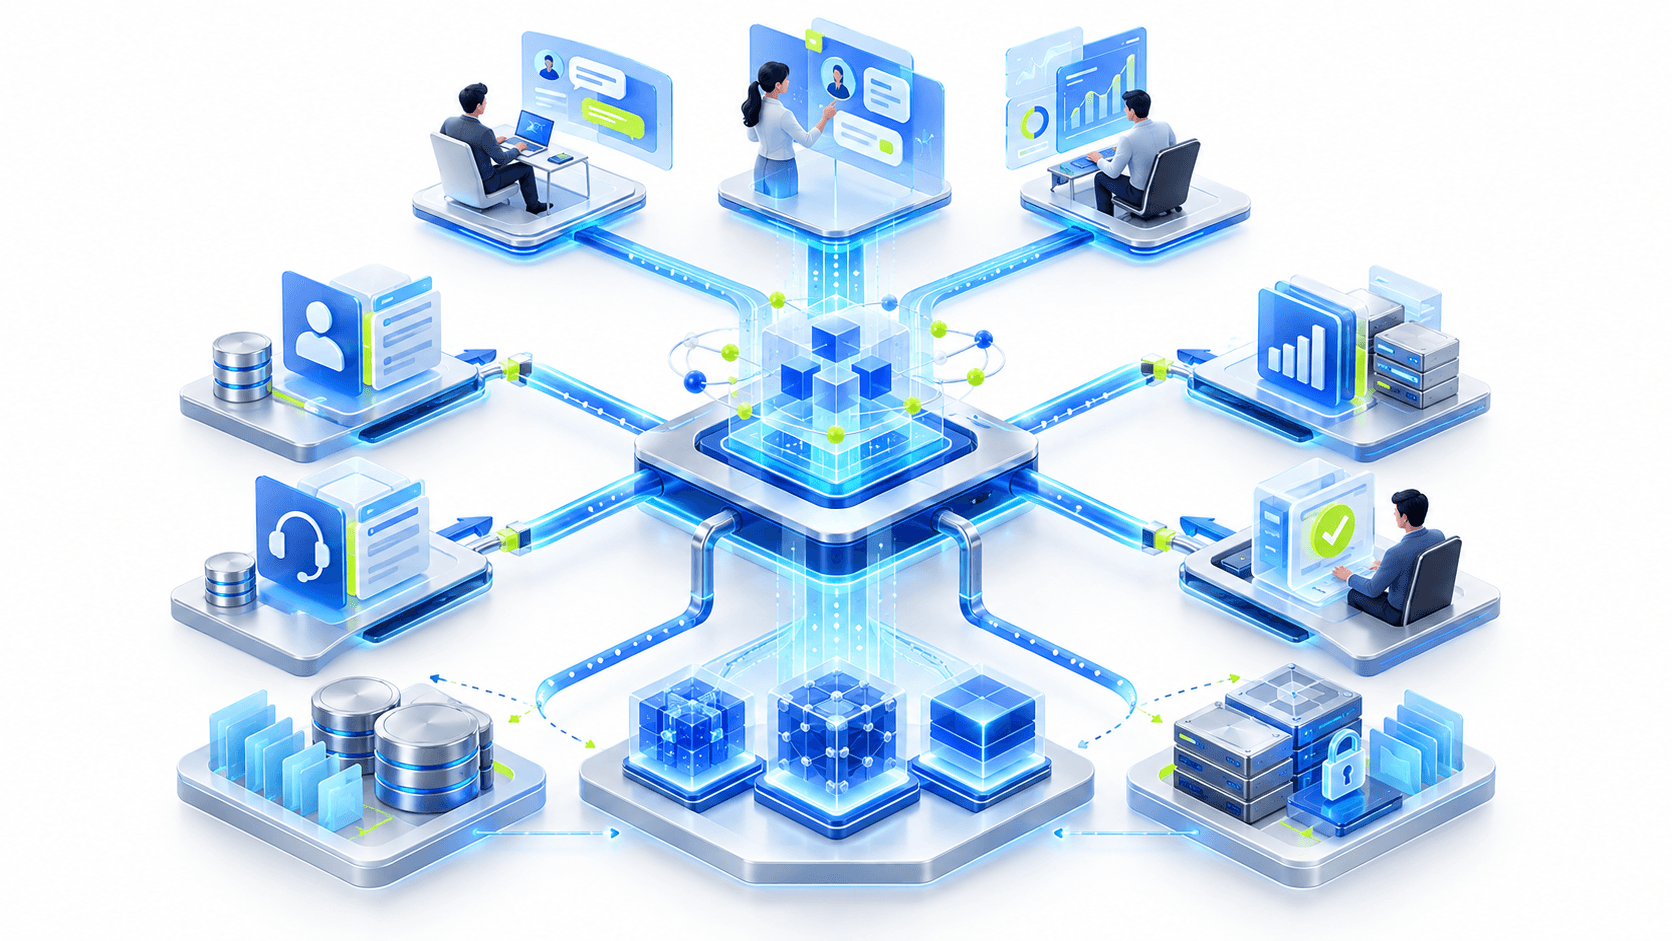
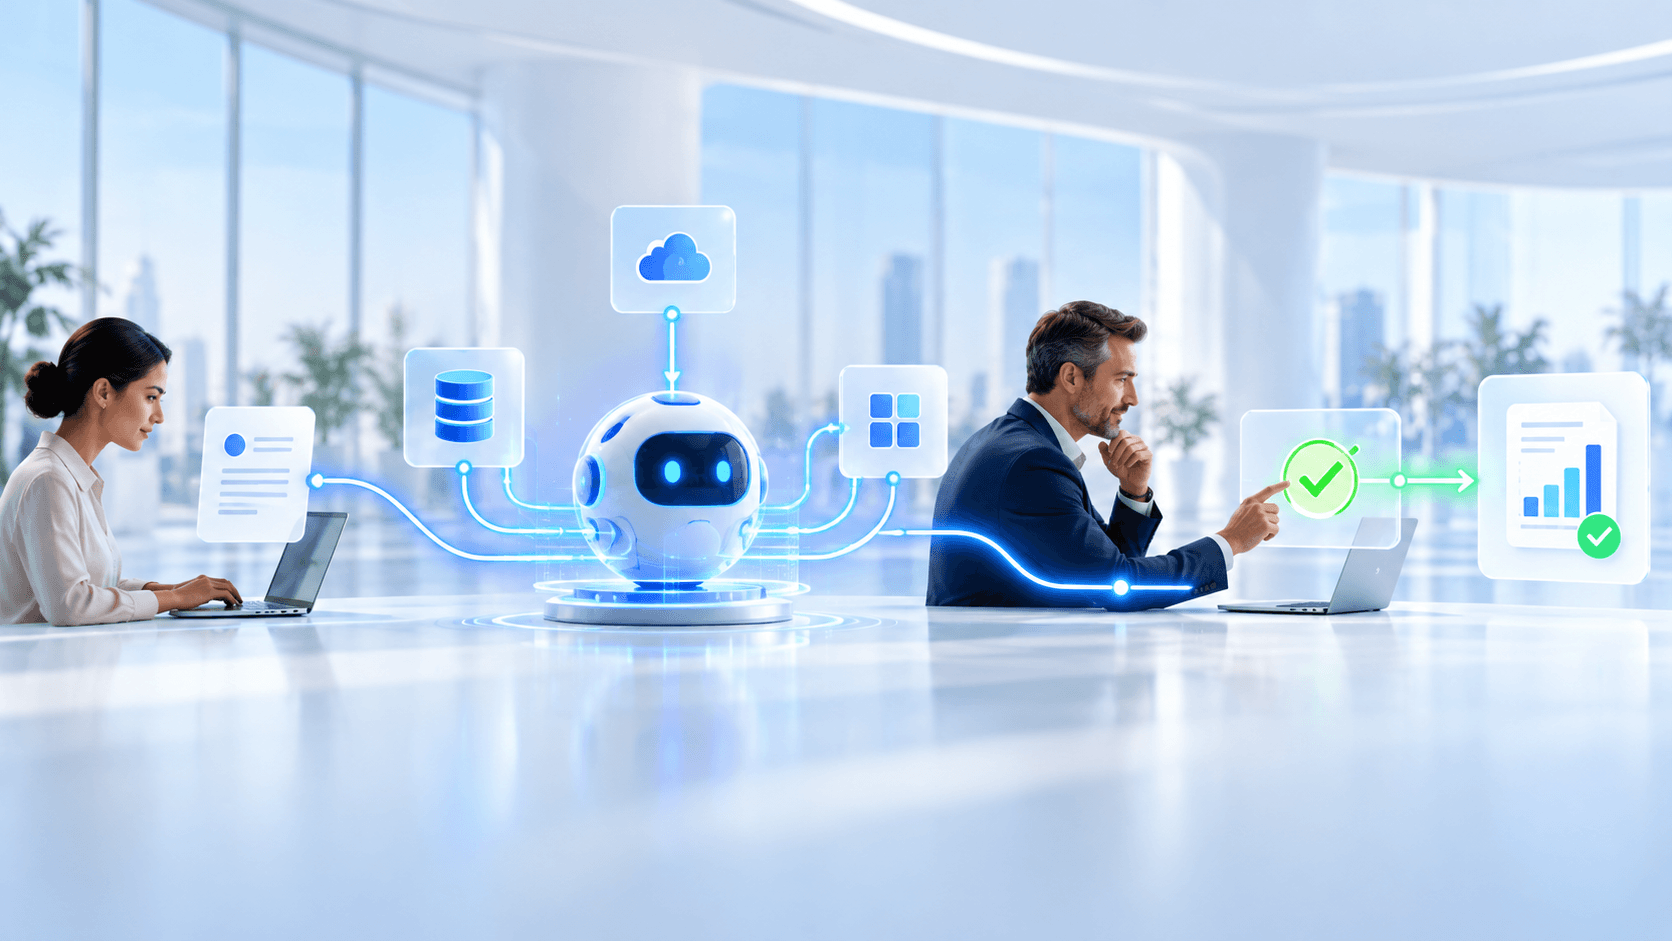
For enterprise teams planning for 2027, the most useful question is unlikely to be “Which agent should we buy?” It is “How will this work move across our systems, identities, policies, and people?” Agentic AI can gather context, choose from approved tools, complete bounded steps, and explain the result. The operational value comes from coordinating those capabilities reliably, not from giving a model unrestricted authority.
A reasonable trend outlook is that agentic workflow automation will increasingly be judged as an architecture and operations capability. Buyers will compare orchestration, observability, identity, evaluation, and integration alongside model quality. Autonomous AI agents and multi-agent systems may fit some complex work, but they add handoffs and failure modes. Treat that direction as a planning hypothesis to validate against your own software, regulations, and business demand.
Map the work before selecting an agent
A production agent needs an explicit operating envelope. Limit which data it can access, which tools it can call, and which actions it can complete without approval. Keep consequential or ambiguous decisions reviewable by the people accountable for the process.
These boundaries make the system easier to test and explain. They also give teams a sensible way to increase autonomy over time, based on observed performance rather than optimistic assumptions.
Measure the outcome, including the exceptions
Track completion rate, time saved, quality, escalation frequency, and the cost of handling failures. A system that performs well only on ideal inputs is not yet improving the whole workflow.
The practical path is to pilot with a narrow scope, review real traces with process owners, and expand only when the result is dependable. That is how agentic AI becomes an operational capability instead of a compelling demo.
Explore: AI agent platform services
Map the workflow and its decision rights
Start with one process that has a clear owner and recurring friction. Draw the current path from trigger to completion, including the systems people open, the information they look up, the decisions they make, and the points where work waits. Include exceptions rather than designing only for the happy path. A customer-support request, for example, may need identity verification, entitlement lookup, policy checks, a proposed answer, and a human escalation when confidence is low.
Then define decision rights. Which steps are clerical, which require professional judgment, and which create a commitment to a customer or employee? That boundary determines the useful role of the agent. It may collect context and prepare a recommendation while a person approves the action. A process map also reveals where ordinary workflow automation is simpler, cheaper, and more predictable than an LLM-based system.
Give the agent a narrow tool contract
An agent should receive a small set of named tools, each with a specific purpose and typed inputs and outputs. Prefer a read-only lookup tool over a broad database credential. Separate the ability to draft a transaction from the ability to submit it. Validate inputs and outputs at the integration boundary, and return structured errors that let the orchestrator recover or ask for human help.
Permissions should follow the user and the task. Use short-lived credentials, role-based access, and service identities rather than shared secrets embedded in prompts. Apply limits on call count, time, token use, and financial exposure. These controls reduce the blast radius if a model misunderstands instructions or retrieved content contains malicious directions. A tool contract makes security testable and clarifies who owns each integration.
Treat context and memory as governed data
Agent quality depends on the context supplied at each step. Retrieve only information needed for the task, keep source references alongside extracted facts, and respect the permissions of the requesting user. Do not assume that a model can infer which document is current or authoritative. Establish metadata for owner, effective date, business unit, sensitivity, and retention where appropriate.
Be deliberate about memory. A workflow may need short-lived state to continue a multi-step task, but that does not mean it should retain every conversation indefinitely. Define what is stored, for how long, who can inspect or delete it, and whether the information can be reused in another session. These decisions belong in the data governance and privacy design, not as afterthoughts once a pilot is popular.
Explore: AI technology stack
Design for failure, interruption, and recovery
Production workflows encounter rate limits, unavailable APIs, partial writes, duplicate events, malformed documents, and changing user intent. Make steps idempotent where possible so a retry does not submit the same payment or service request twice. Record state transitions and correlation IDs, set timeouts, and decide which failures should retry, stop, or route to a queue for review.
A person should be able to take over without reconstructing the entire interaction. Provide a concise handoff packet with the goal, gathered evidence, attempted actions, unresolved questions, and relevant source links. When the process resumes, the system should know which actions already succeeded. Recovery design is not glamorous, but it is often what separates a trustworthy AI service from an unreliable demo.
Evaluate behavior before expanding autonomy
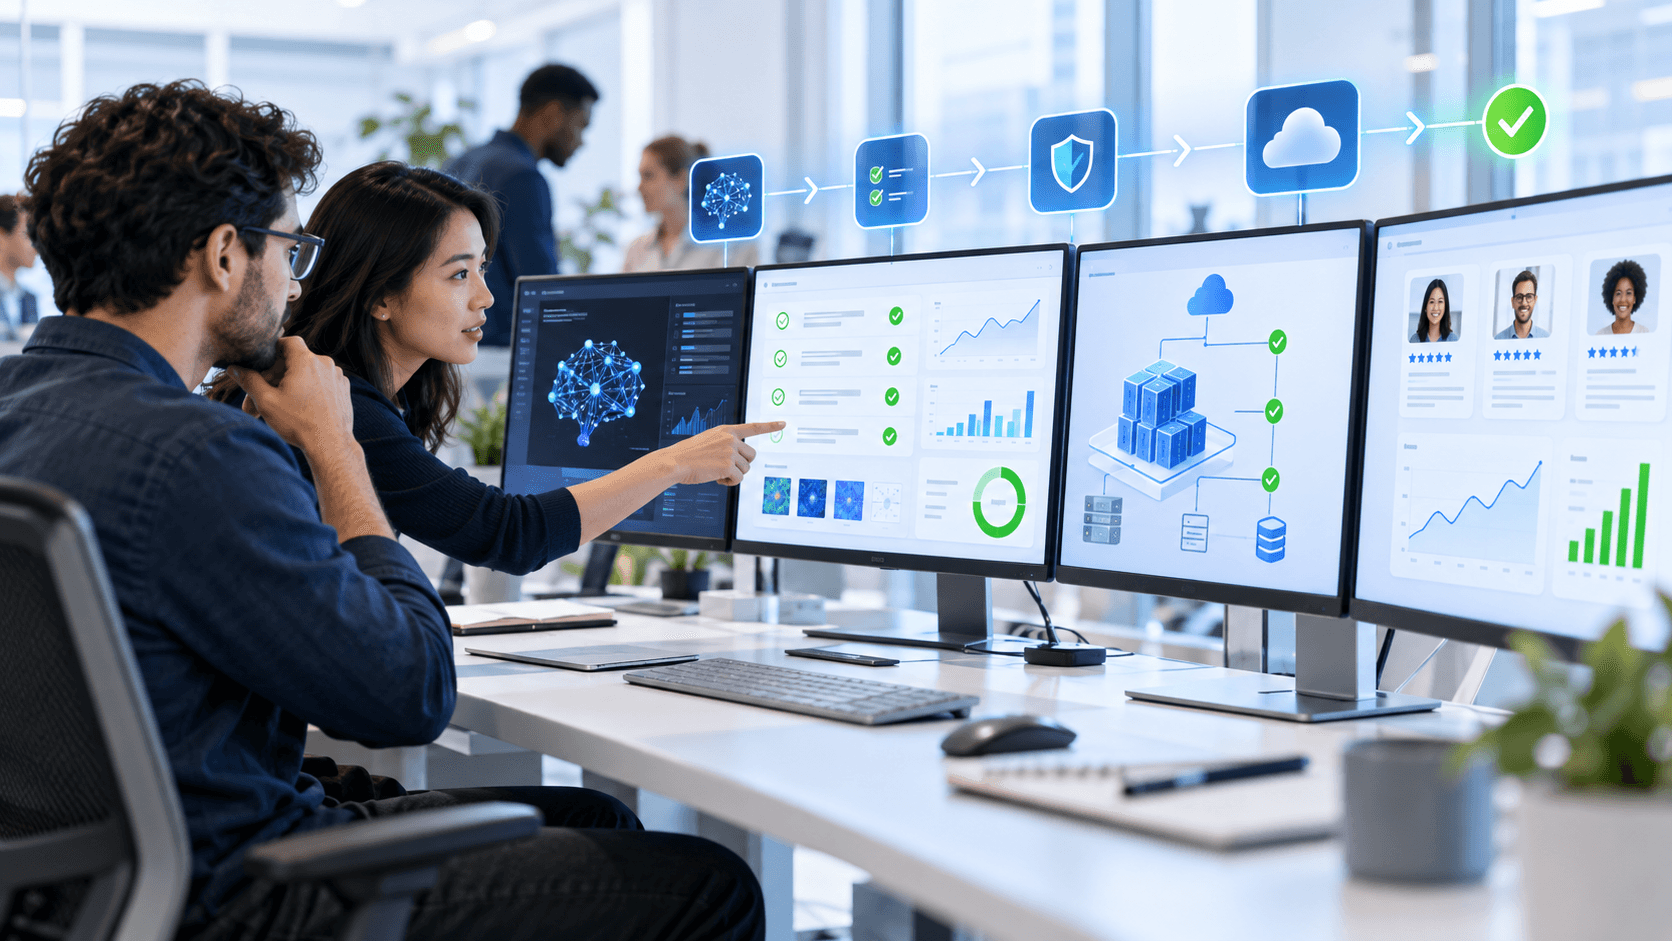
Build an evaluation set from real, permissioned cases and include ordinary requests, ambiguous instructions, edge cases, policy conflicts, adversarial content, and tool failures. Have process experts define what a correct outcome looks like. Evaluate the complete workflow, not only the model response: Was the right source retrieved? Was the correct tool selected? Did the agent stop when approval was needed? Was the final record accurate?
Run a staged release: offline tests, shadow mode, a small user cohort, and only then a broader rollout. Compare against the baseline on cycle time, successful completion, rework, escalation quality, customer impact, and total cost. Review failures with the people who own the work. Increase autonomy only when the evidence supports it, and preserve a kill switch and rollback path throughout the lifecycle.
Make ownership part of the design
Every production agent needs a business owner who can decide whether its behavior is acceptable, a technical owner who can change the system, and an operations contact who can respond when it fails. Define how incidents are reported, what evidence is retained, how users appeal or correct an outcome, and who can pause the system. Ownership should be visible to the people who depend on the process.
Review the agent as the surrounding business changes. A new policy, tool permission, model version, or data source can change behavior even when the user interface stays the same. Schedule recurring evaluation and access reviews, and retire unused tools. This discipline lets an organization adopt agentic AI confidently without treating autonomy as a one-time configuration decision.